← Back to blog
Infrastructure and connectivity
How to securely connect multiple company sites in Colombia
Why growing without a prepared network turns every new site into a risk, and which architecture helps avoid it.
Opening a new site usually looks like an operational decision: more space, closer to customers and more capacity. But if the network isn't ready for it, that same site can become a new point of risk for the whole organization.
As a company grows, so does the need to connect offices, warehouses, plants, points of sale or operations centers in different cities. At first the challenge seems simple: everyone needs access to the same applications, files and corporate systems.
However, connecting multiple sites without the right architecture usually results in slowness, duplicated information, insecure access and greater cybersecurity risks.
The real goal isn't just connecting sites, but making the entire organization operate as a single secure, controlled network that is ready to grow.
That's why site-to-site connectivity must be designed with security, availability, performance and centralized management in mind, not as a solution pieced together on the fly.
When each site works like an island
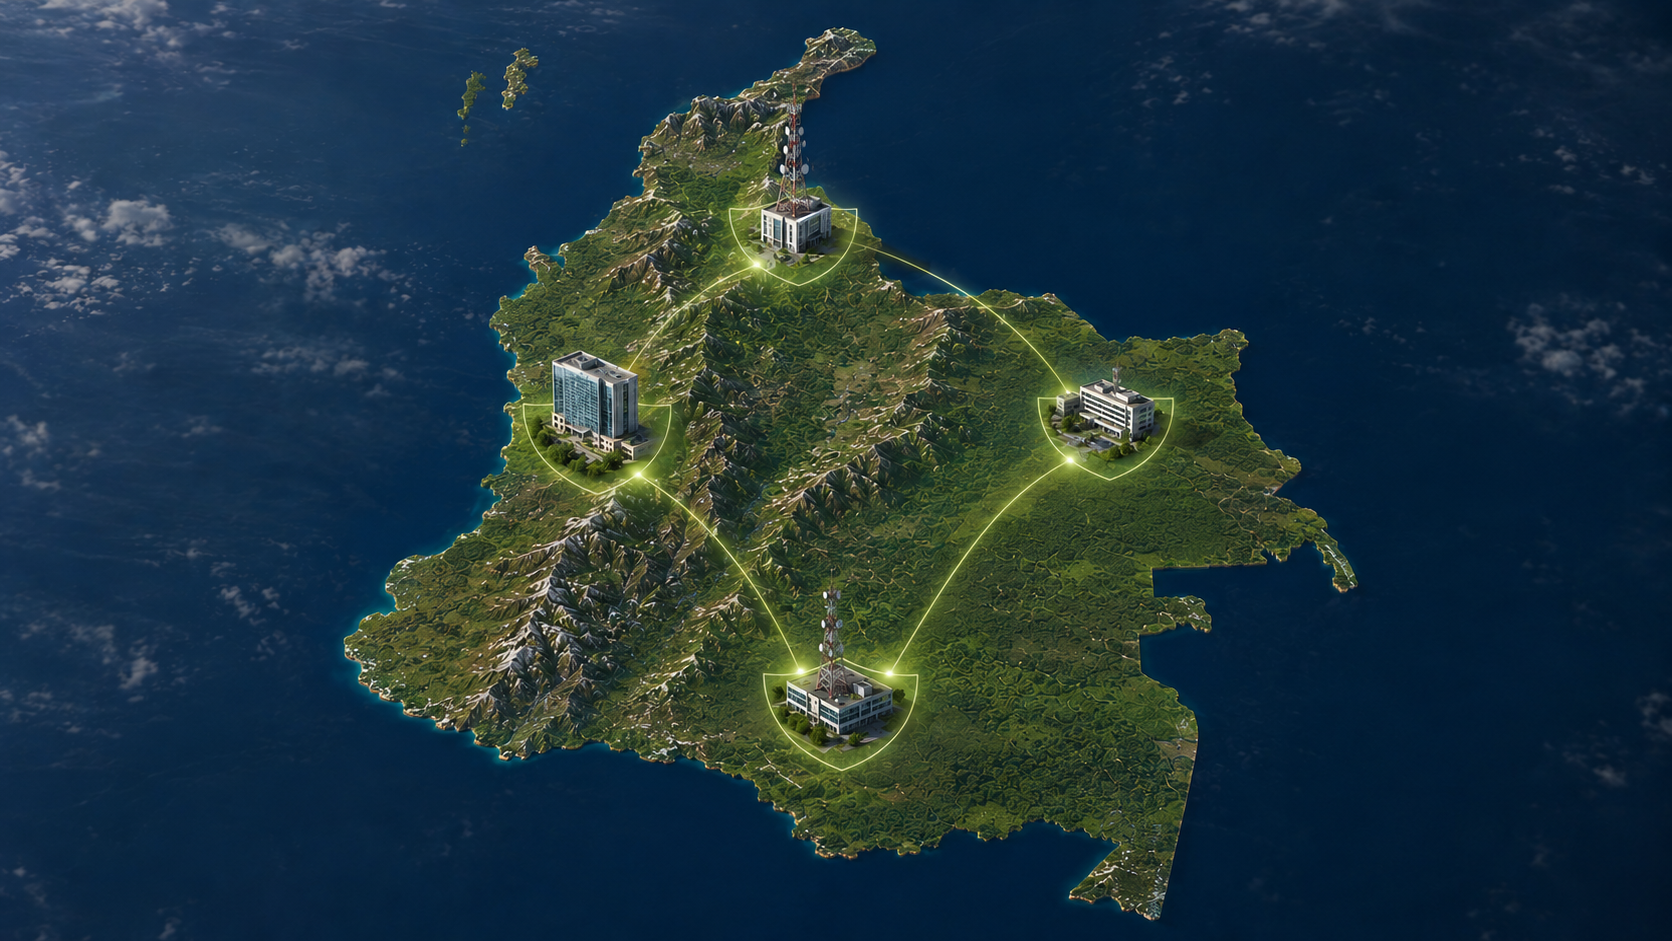
A headquarters in Bogotá, a warehouse in Medellín, a sales office in Cali or an operations point in Ibagué may belong to the same company and still operate in isolation if there is no well-designed corporate network.
When this happens, teams look for quick fixes: they share files through unauthorized channels, improvise remote access or rely on configurations nobody ever fully documents. Over time, these informal solutions create four problems that reinforce each other:
Scattered information
Files and data end up spread across sites without centralized control.
Insecure access
Users connect through methods that don't meet minimum security policies.
Poor performance
Critical applications run slowly because traffic isn't prioritized.
Greater complexity
IT manages multiple environments without a unified view of the corporate network.
The trickiest part is that these problems grow silently. By the time the organization notices them, the network has already become an operational risk factor, and fixing it costs much more than designing it properly from the start.
The root of the problem isn't only technical: nobody defined, from the beginning, what that network needed to deliver.
Connecting sites isn't just joining dots on a map
Many companies believe connecting offices simply means enabling communication between locations. In reality, a corporate network across sites must answer more important questions: who can access the information? From where do they connect? Which applications are critical? And what happens if a site loses connectivity?
These questions make the difference between a basic connection and a secure enterprise architecture. A well-designed network protects data, controls access, prioritizes critical applications and lets the business keep operating even when one location has problems.
With those answers clear, the natural first technical step is an enterprise VPN.
The first step: a well-implemented enterprise VPN
For many organizations, an enterprise VPN is the starting point for securely connecting sites. This technology creates encrypted tunnels between locations, protecting the information that travels over the Internet.
But not all VPNs offer the same level of security. A poor implementation can become a gateway for unauthorized access or a point of failure for the operation. Before considering it secure, it's worth confirming that it has:
- Proper encryption to protect information in transit.
- Strong authentication that validates users and devices.
- Access policies based on business roles and needs.
- Monitoring of active connections and security events.
- Segmentation that avoids exposing internal resources unnecessarily.
A well-implemented VPN may be enough for many companies, but it's best understood as part of a broader connectivity and cybersecurity strategy, not as the final destination.
When the company grows, the network must evolve too
As sites, users, applications and cloud services increase, a basic architecture can fall short. That's where technologies like SD-WAN make it possible to manage multiple links, optimize traffic and improve the user experience.
- Better use of links: leverages multiple connections and chooses the most efficient routes.
- Application optimization: prioritizes critical services such as ERP, cloud and videoconferencing.
- Integrated security: provides advanced protection against internal and external threats.
- Centralized management: IT manages policies, availability and performance from a single view.
But connectivity alone still doesn't answer the underlying question: who should have access to what. That question is answered by security, not just by the network.
Security must accompany every connection
Every newly connected site expands the organization's exposure surface. That's why allowing communication between offices isn't enough: you also need to control who accesses, from which device, to which resource and under what conditions.
This approach aligns with Zero Trust, where no user, device or location is automatically considered trustworthy.
Isn't based only on connecting. It's based on verifying, controlling, monitoring and protecting every access.
The difference between having connected sites and having a secure enterprise network
When connectivity is designed properly, sites stop working as separate points and become part of a more efficient, secure and scalable business operation.
Are your sites really connected securely?
At ECOMIL we help design enterprise connectivity architectures for organizations with multiple sites, integrating VPN, SD-WAN, perimeter security, monitoring and centralized management.
The goal isn't just to connect offices: it's to protect the operation, improve performance and prepare the infrastructure for growth.
Request an assessment